
Information Security Engineer
Bengaluru · Mid Level
Applicants who checked fit first are 3.1× more likely to hear back
Your score for this role already exists
ASAI compared this JD against 41 signals - skills, seniority, domain, stack overlap etc. Add a resume and it unlocks in about 30 seconds.
No credit card · 1 tap with Google
What we know about this role
LOW
bureau is showing limited hiring activity lately. Expect slight delayed response.
First 72 hours
Window passed - posted 293d agoEarly applicants get seen before the pile builds.
Not a repost
The first time we've seen this listing - it hasn't been closed and reopened.
Skills required
20 listedYou almost certainly match several of these already. Unlock your skill map to see the matches, the gaps, and what to fix first.
Job description
About Bureau
Bureau is a unified risk decisioning platform for Compliance, Fraud, and Transaction risks. Our platform is a single decision-making engine, powered by a 1 billion+ identity knowledge graph. Over 150 Banks, fintechs, retailers, and digital platforms use Bureau to verify identities faster and stop fraud earlier globally.
Bureau has raised $50M+ from renowned Silicon Valley and global investors including Sorenson Capital and PayPal Ventures and is expanding rapidly from APAC to Americas, Europe, and beyond.
Why Bureau?
Bureau is building the infrastructure that makes digital identities and transactions safe and trustworthy for billions of people. The mission is big, the problems are complex, and the impact is real.
We hire people who want that level of responsibility. People who move fast, build systems from scratch, and care deeply about turning strategy into execution. If you want predictability or narrow scope, this won't be your place. If you want to shape how a scaling global company operates—keep reading.
About the Role - Information Security Engineer
We are looking for a Security Engineer who can own both the hands-on technical security stack and our governance/compliance programs.
What you’ll be doing
In this role, you will:
Harden and monitor our cloud & container infrastructure (AWS/EKS, endpoints, network).
Run vulnerability management, security tooling and incident response.
Help maintain our ISMS and support audits (ISO 27001, SOC 2, RBI, DPDP, etc.).
This is ideal for someone who doesn’t want to be only “checklist GRC” or only “pure blue-team”, but wants a blended role across security engineering + GRC.Key Responsibilities
1. Cloud & Infrastructure Security (Hands-on)
Work with DevOps to secure our AWS/EKS environment:
IAM hardening, security groups, VPC, KMS, S3, RDS, etc.
Review infra-as-code (Terraform/Helm) for security issues and misconfigurations.
Own or co-own key security tools:
Endpoint / EDR (e.g., CrowdStrike / SentinelOne),
Cloud security (CSPM / CNAPP, GuardDuty, Security Hub, WAF, etc.),
Container / runtime security where applicable.
Implement and maintain logging & monitoring for security events (CloudTrail, ALB/NLB logs, K8s logs, etc.), and integrate them with SIEM / alerting.
2. Vulnerability Management & Security Operations
Own the vulnerability management lifecycle:
Run periodic scans for cloud, endpoints, containers and apps.
Triage findings, prioritise based on risk, and drive closure with engineering.
Coordinate external pentests / bug bounties and track remediation.
Support incident response:
Help investigate alerts, gather evidence, and contribute to RCA and CAPA.
Maintain and update incident runbooks.
3. Governance, Risk & Compliance (ISMS, Audits, DPDP)
Maintain and enhance the Information Security Management System (ISMS):
Policies, procedures, SoA, risk register, control evidence and audit trails.
Support internal and external audits: ISO 27001, SOC 2, RBI/CERT-In, Data Protection.
Prepare and manage audit evidence, observations, closure reports and certification documentation.
Assist with risk assessments:
Maintain the risk register, risk treatment plans and residual risk reviews.
Conduct vendor security due diligence and maintain vendor security records (MSA, NDA, DPA, DPIA, etc.).
Support privacy & regulatory compliance operations (GDPR/DPDP basics: retention, consent, grievance logging).
4. Access, Asset & Control Assurance
Participate in and help automate access reviews, asset inventory checks, and configuration compliance checks.
Track control performance (vuln SLAs, access reviews, backup tests, etc.) and ensure gaps are documented and closed.
Maintain security awareness and training trackers (onboarding, annual refreshers, phishing simulations).
What You’ll Bring
Bachelor’s degree in Computer Science, IT, Cybersecurity or related discipline.
~4 years of experience in security engineering, cloud security, or GRC/compliance (any mix, but must be comfortable hands-on).
Good understanding of:
Security engineering fundamentals: Linux, networking, IAM, encryption, least privilege.
Cloud platforms (AWS preferred; GCP/Azure a plus) and their security services.
Core frameworks: ISO 27001, SOC 2, basic risk management and audit lifecycle.
Comfortable with:
Writing/debugging basic scripts (Bash/Python) for automation and data extraction.
Tools like Jira, Confluence, Excel/Sheets and at least one GRC / security platform (e.g., Scrut/Drata/Secureframe, etc.).
Strong documentation skills and ability to talk to both engineers and non-technical stakeholders.
Preferred (Good to Have) / Willing to Learn
Cloud security certifications (e.g., AWS Security / AWS Cloud Practitioner).
ISO 27001:2022 Lead Auditor/Implementer, CompTIA Security+, ISC2 CC.
Experience with:
EDR/XDR tools,
CSPM/CNAPP (e.g., Wiz, Prisma, Defender for Cloud),
SIEM, WAF, runtime/container security (Falco, etc.).
Exposure to GDPR/DPDP or other data protection regimes.
Who You Are
You enjoy both:
Getting your hands dirty in logs, configs and cloud consoles, and
Keeping things clean in policies, risk registers and audit trackers.
You’re structured and process-oriented, but still pragmatic and capable of shipping improvements.
You’re comfortable collaborating with DevOps, backend, data, HR and legal to get security actually implemented, not just written down.
You want to grow into either Security Engineering leadership (owning tools/architecture) or GRC leadership (owning audits and certifications) over the next few years.
Our Culture
We hire self-motivated people and get out of their way
We value performance, not hours worked
Speed, ownership, and impact matter most
Compensation
Competitive salary + potential equity
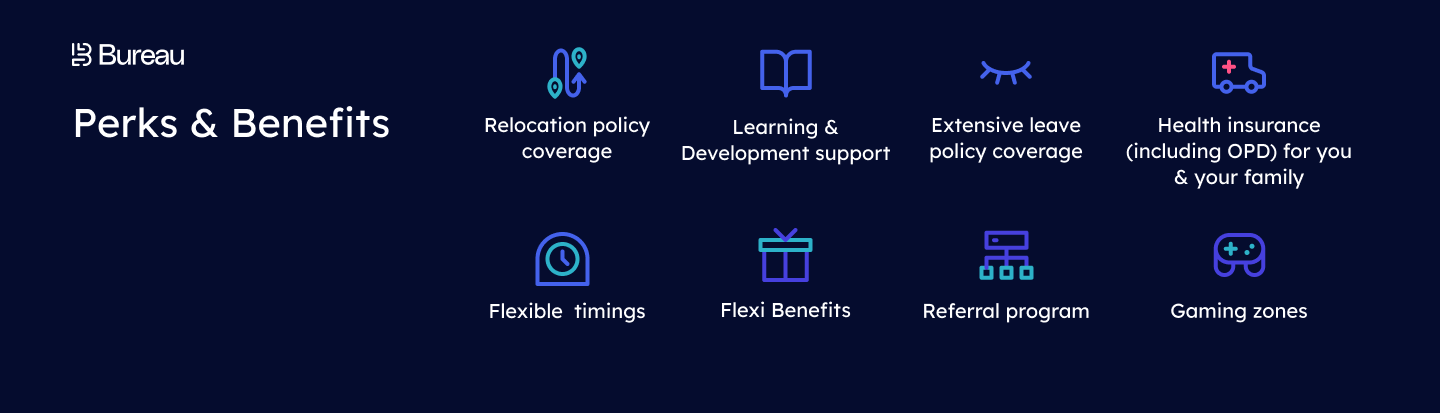
Health benefits, flexible PTO, learning budget
Free · no signup
Get tomorrow's jobs before you have to search
Daily job drops, skill trends and free resources - posted straight to the group. Leave any time.
No spam. Just jobs and resources.
Why people use ASAI
Someone shared one job with you. ASAI keeps finding the rest.
Scored, not searched. Every role ranked against your actual profile.
Alerts as often as hourly. Reach new roles while the pile is still small.
Skill gaps, spelled out. See exactly which requirements you don't meet yet.
Verified jobs, only. Say no to ghost jobs. Your time deserves respect.
More Security Engineer roles in Bengaluru
See allKeep browsing